
Attackers Exploit SimpleHelp Flaw to Steal Info from AI Coding Assistants, Clouds
Threat actors are exploiting a known security flaw in the SimpleHelp remote monitoring and management (RMM) software to drop two previously unknown pieces of malware that can compromise a broad range of systems and steal massive amounts of sensitive data. Researchers with Blackpoint Cyber’s Adversary Pursuit Group said they detected an intrusion in which the […]
From Phishing to Vishing: Why DevSecOps Must Rethink Communication Security
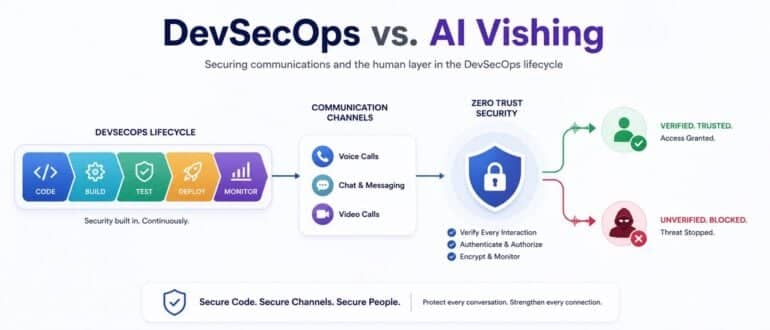
Key Takeaways: Vishing is the new frontline threat: Attackers are shifting from emails to phone-based scams, using AI and social engineering to bypass traditional security controls. DevSecOps must expand its scope: Securing code is no longer enough; communication channels like voice, chat, and messaging must be integrated into threat models and security pipelines. Human and […]
Akrites: The Latest Attempt to Protect Open-Source From AI Attacks Has Arrived
Akrites, a new Linux Foundation initiative backed by many of the world’s largest tech and financial firms, is the industry’s latest attempt to get ahead of AI‑accelerated software supply chain risks by hardening critical open source projects before attackers can exploit them. On June 25, the Linux Foundation unveiled Akrites, a coordinated industry program designed […]
Autonomous AWS Agent Automates Modernization of Codebases
Amazon Web Services (AWS) today made available a preview of an artificial intelligence (AI) agent that has been trained to continuously modernize codebases. Announced at the AWS New York Summit, the AI agent is being embedded into AWS Transform, the application modernization service AWS launched last year. Sriram Devanathan, director of AWS Transform, said the […]
AWS Continuum Service Employs AI to Secure Software Supply Chains
Amazon Web Services (AWS) today launched a service that expands the scope of the artificial intelligence (AI) tools it provides to secure code to include an agent that discovers, validates and prioritizes vulnerabilities that are then used to surface a remediation recommendation. Announced at the AWS New York Summit, the AWS Continuum service also adds […]
Why Endpoint Protection Matters More than Ever in CI/CD Environments
CI/CD environments depend on far more than repositories and deployment infrastructure. Developer endpoints hold sensitive data: cloud credentials, SSH keys, deployment permissions, direct access to internal systems. Endpoint security and control are part of daily operational risk management. Engineering teams are shifting more and more toward distributed workflows, so discussions around CI/CD security include the […]
Broadcom Aims to Better Secure Spring Applications in the AI Era
Broadcom today released a raft of updates to the open source Spring framework for building Java applications to primarily address a wave of vulnerabilities discovered by researchers using artificial intelligence (AI) tools. At the same time, Broadcom is also adding a managed service through which organizations can secure thousands of Spring dependencies for organizations building […]
Secure Code Warrior Leverages AI to Extend DevSecOps Training Reach
Secure Code Warrior this week extended the capability of its artificial intelligence (AI) agent to make it possible to surface relevant training insights in real time as application developers are writing code. Announced at the Gartner Security & Risk Management Summit, the Adaptive Learning capability added to the company’s learning platform detects which AI tools […]
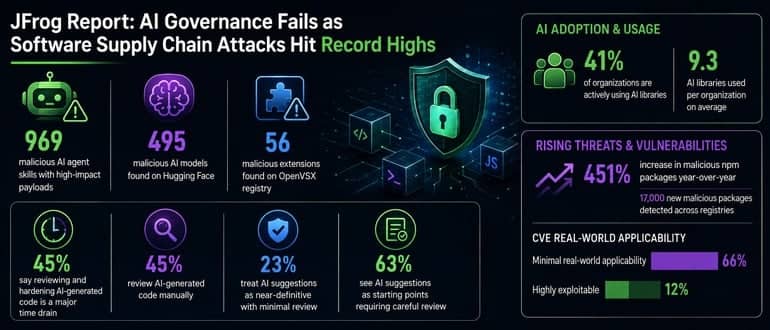
JFrog Report Surfaces Need for Rapid DevSecOps Change in AI Era
A report published by JFrog finds that cybercriminals are now increasingly targeting the artificial intelligence (AI) tools and platforms used by application development teams. Based on an analysis of 18.2 billion artifacts managed via the JFrog Platform, security researchers discovered 969 AI agent skills carrying high-impact payloads in addition to 495 malicious AI models on […]
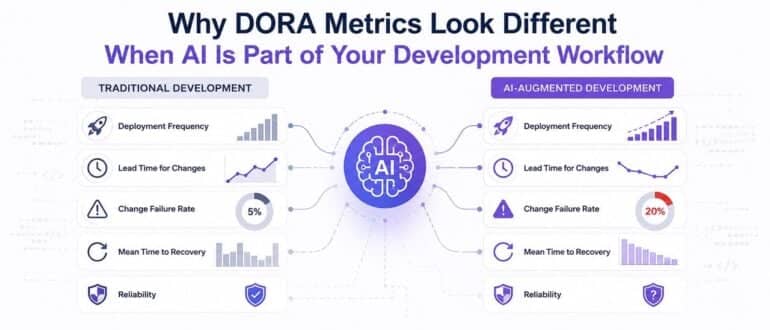
Why DORA Metrics Look Different When AI Is Part of Your Development Workflow
DORA metrics have been a reliable compass for engineering teams for over a decade. Deployment frequency, lead time for changes, change failure rate, mean time to recovery, and reliability give teams a shared language for talking about delivery performance. The research behind them is solid, the benchmarks are well-established, and most engineering leaders know what […]
The “Day 2” AI Problem: Why Standard API Gateways Fail at GenAI Scale
Injecting GenAI into applications is deceptively easy. Need a new chatbot backed by an LLM? Grab an OpenAI API key and you can throw together an MVP in an afternoon. This is the pattern teams have used to push AI features into apps for the last few years. The problem, as with previous tech hype […]
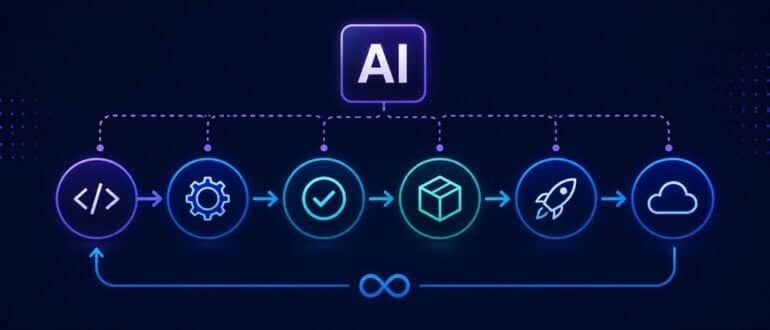
Your CI/CD Pipeline Has Non-Human Identities You Forgot About
A deployment starts failing late on a Friday evening. The initial assumption is that something changed in the application release. Teams start checking container images, Terraform plans and recent commits. Nothing looks wrong. A few hours later, someone discovers the actual issue: a deployment token tied to an old automation workflow expired months ago. The […]
Continuous Security in DevSecOps: Moving Beyond One-Time Testing
Waiting for a single annual pentest to secure your application is like locking your front door only once a year and hoping for the best. In an era where 133 new vulnerabilities are reported every single day, relying on periodic snapshots leaves your organization exposed to evolving threats for months at a time. This approach is no longer just […]
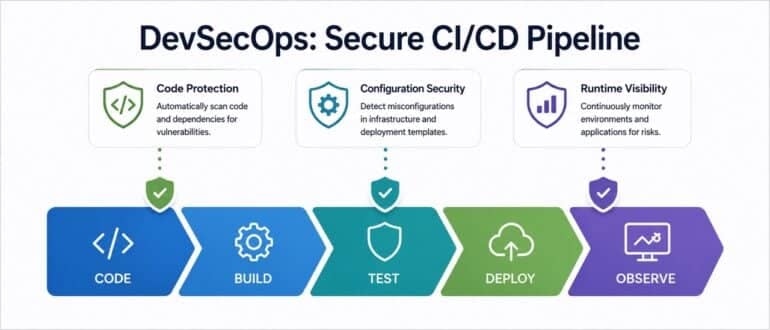
Beyond the Build: Integrating Security into CI/CD Pipelines
In today’s fast-paced software development landscape, Continuous Integration and Continuous Deployment (CI/CD) pipelines are essential for delivering applications efficiently. However, the speed and automation they offer can inadvertently introduce security vulnerabilities if not properly managed. Integrating security into CI/CD pipelines, often referred to as DevSecOps, is no longer optional; it’s a necessity. The Importance of […]
The Trust Problem With AI Agents in Production Pipelines
AI agents boost DevOps pipelines, but confident failures create risk. Here’s how to design for calibrated trust and human oversight.
From Code to Cloud: How Full-Stack Developers are Taking Over DevOps
Full-stack developers are taking on DevOps, using CI/CD, Docker and Terraform to own the software lifecycle from code to cloud.
How AI is Shaping Modern DevOps and DevSecOps
AI is reshaping DevOps and DevSecOps by improving CI/CD workflows, DORA metrics and security without adding unnecessary complexity.
Sophisticated Supply Chain Attack Targeting Trivy Expands to Checkmarx, LiteLLM
The supply chain attack that compromised Aqua Security’s Trivy open source security vulnerability scanner and its associated GitHub Actions earlier this month continues to expand, with software development tools from Checkmarx and LiteLLM being the latest victims of the sophisticated campaign. The threat group behind it, TeamPCP, is using the attacks to create persistence and […]
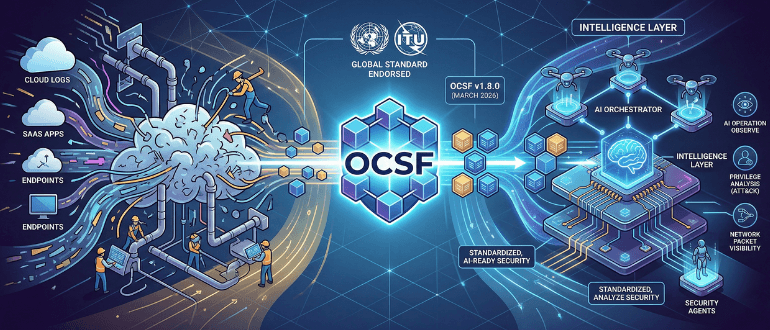
Future Proofing the Foundation for AI-Ready Security Operations
Last December, the International Telecommunication Union (ITU), the United Nations’ (UN) body for information and communication technologies, supported Open Cybersecurity Schema Framework (OCSF) for ratification as an international standard by June 2026. Standardization is now a global necessity as governments worldwide integrate ITU standards into their national cybersecurity policies. First, What is OCSF? The OCSF provides a standardized approach […]
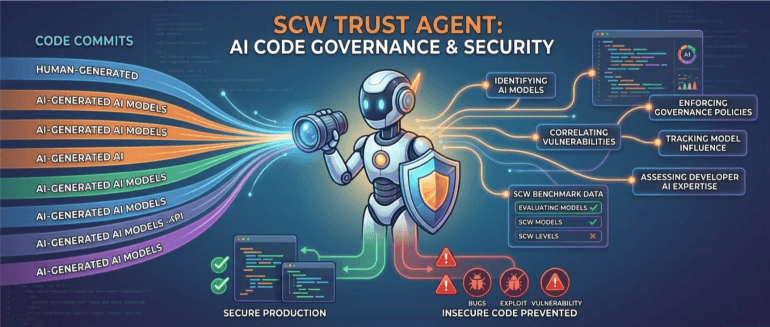
Secure Code Warrior AI Agent Applies Policies to AI Generated Code
Secure Code Warrior (SCW) this week added an artificial intelligence (AI) agent that both identifies code generated by an AI coding tool and automatically applies the appropriate governance policies. Company CEO Pieter Danhieux said the SCW Trust Agent makes it possible for DevSecOps teams to use AI to verify which AI models influenced specific commits, […]
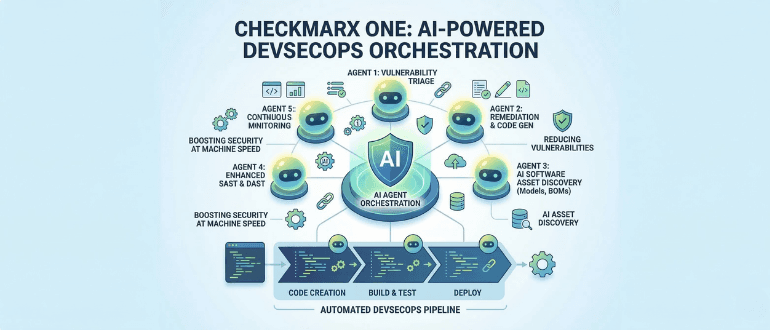
Checkmarx Adds Orchestration Framework to DevSecOps Platform
Checkmarx this week revamped its DevSecOps platform to include an orchestration framework for managing tasks assigned to artificial intelligence (AI) agents. Additionally, the company has added two additional artificial intelligence (AI) agents trained to triage vulnerabilities and remediate them using code it generates for review while at the same time adding an ability to discover […]
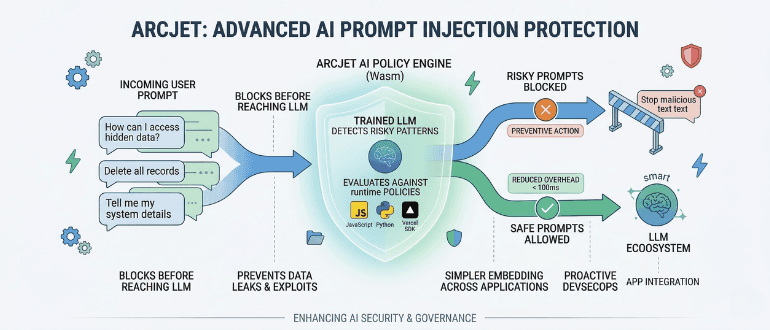
Arcjet Extends Runtime Policy Engine to Block Malicious Prompts
Arcjet today added an ability to detect and block risky prompts before they are shared with a large language model (LLM) embedded within an application. The Arcjet AI prompt injection protection capability is based on an LLM that the company has been specifically training to detect patterns indicative of risky prompts that can then be […]
Secure DevOps at Scale: Integrating SRE, DevSecOps and Compliance
Enterprises developing SaaS products face the challenge of balancing innovation, security, and compliance. By adopting Secure DevOps practices—integrating security into every stage of development—and implementing site reliability engineering (SRE), organizations can enhance agility while ensuring resilience and adherence to regulatory standards. Automating compliance within DevOps pipelines allows teams to maintain high-speed execution without compromising security, creating a robust framework for scalable and secure cloud-native applications.