
Video Interviews
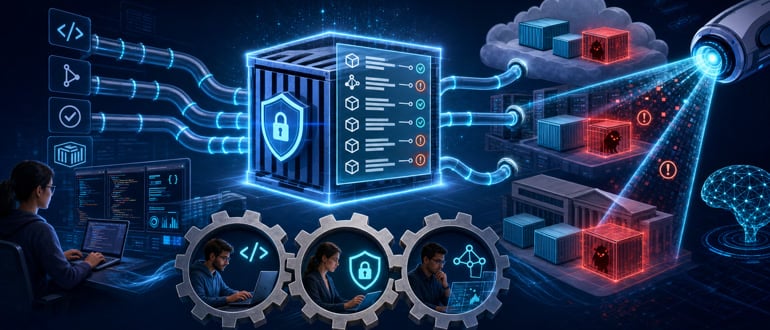
Software Weaponization Raises DevSecOps Stakes
The threat model that DevSecOps teams have been working from for the last decade was built around accidental vulnerabilities — mistakes that needed to be found and fixed before someone exploited them. That assumption is breaking.…